SLCOS · Biometric smartcards · FIDO2 · PKI
Europe’s most secure hardware-rooted authentication.
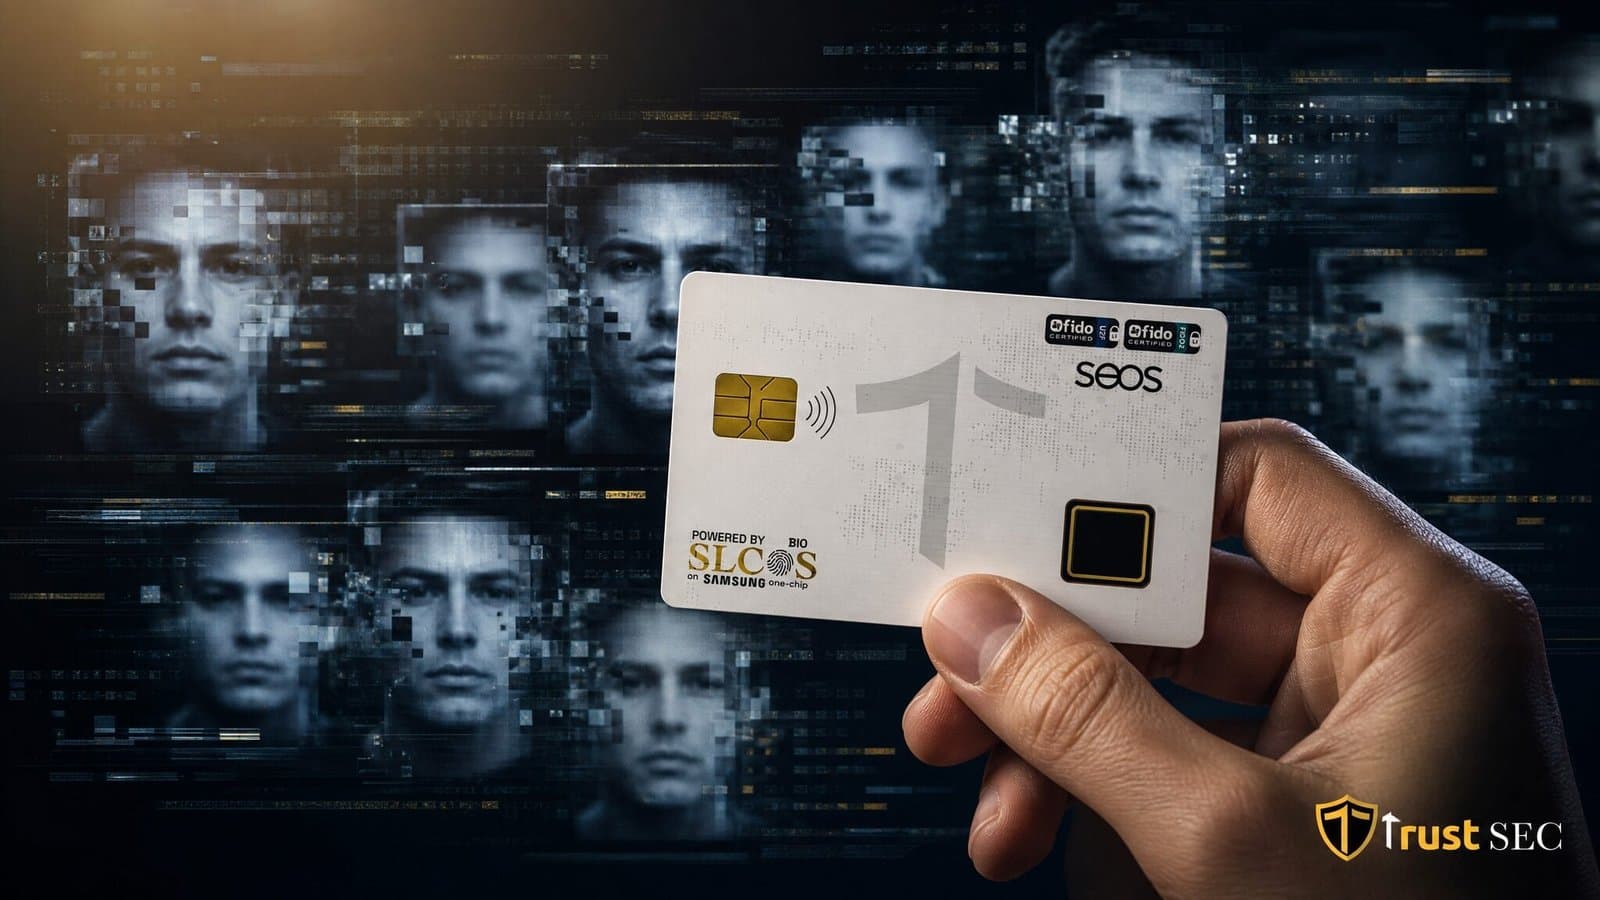
Highly secure hardware and software that secure identities in the digital transformation of governmental and financial services — built on SLCOS, our in-house smartcard operating system, with the fingerprint matched on the card.
SCROLL
Why TrustSEC
Hardware-rooted, from the fingerprint to the chip.
IN THE EU
01 / THE PROBLEM
A shared password is a door your auditor cannot close.
Every shared secret is an identity your logs cannot resolve to a person. Passwords and one-time codes leave staff exposed to phishing, credential theft and account takeover — and an assessor looks for that gap first.
A card that holds its own key, and a fingerprint that never leaves it, close the gap by making the credential physically unshareable.
Solutions
Four doors, depending on what you need to protect.
Authentication, identification, payment and mobile-app protection — every one built on the same in-house operating system.
Authentication
FIDO2, PKI, access control and OTP — hardware-rooted, with the fingerprint matched on the card.
FIDO2 · PKI · OTP · ACCESSIDENTIFICATIONIdentification
Certificate authority and centralised authentication for national and enterprise scale.
EAL4+ · CWA / ETSIPAYMENTPayment
Payment applets running over SLCOS.
CPACEMOB. APP. PROTECTIONMobile App Protection
Protection for applications that run on devices you do not control.
THE GUARDIAN · ELSIntegrations
One card. Every system that has to trust it.
SLCOS runs several applications side by side in one secure element, separated by GlobalPlatform security domains — so one credential can serve each system below.
Applets are deployed across multiple chip platforms without modification, and SLCOS integrates with multiple biometric sensor and module vendors — protecting the investment and simplifying migration.
All productsOur products
Hardware and software, built on our own OS.
Smartcard OS
Multifunctional biometric smartcard OS that combines the best in security, flexibility and hardware independence.
SLCOSFIDO2 · PKISecurity keys
A wide range of multi-factor and two-factor authentication products: PKI tokens and FIDO2 security keys.
TOKENS · CARDSAUTHENTICATION · PAYMENTApplets
Standard and customised applets that support the latest technology in authentication and payment.
FIDO2 · PKI · CPACETOTP · HOTPOne-time password
OTP turnkey solution: a high-performance backend and a variety of soft and hardware end-user interfaces.
OTP BACKENDLifecycle
The part nobody else explains.
SLCOS supports secure loading, installation, personalisation and post-issuance management — the half of a programme that decides whether it succeeds.
Load
On-card bytecode verification: only valid, trusted applets install.
Install
Security domains delegate each application to its provider.
Personalise
Keys, certificates and credentials written to the card.
Enrol
Fingerprint template created and stored on the card.
Use
Sign, log in, open doors, pay — online or offline.
Manage
Post-issuance updates without re-issuing the card.
Heritage
Twenty-five years of cryptography, in cards still supported.
Compliance hub
The regulations, explained for the people who buy against them.
Deployments
Case studies from the field.
 CASE STUDY · HEALTHCARE
National Healthcare Case Study
Revolutionizing Cybersecurity in Patient Care with TrustSEC Biometric Smartcards Introduction: Cybersecurity at the Core of Healthcare In today’s healthcare environment, …
Read the case study →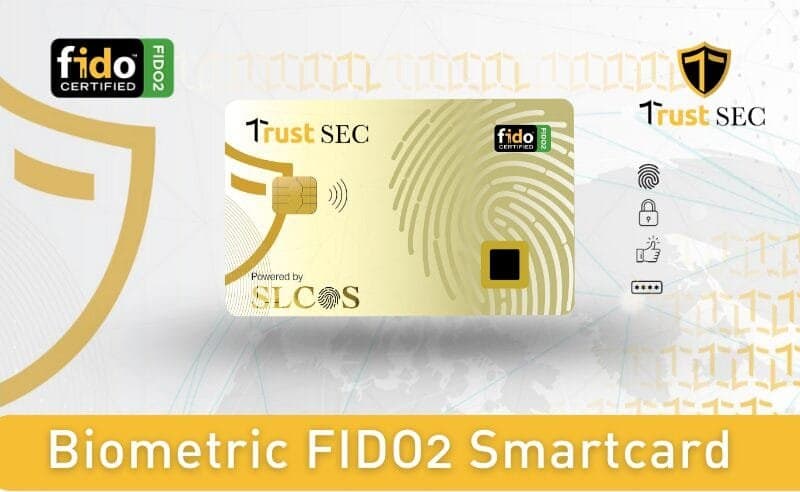 CASE STUDY · ENTERPRISE · MULTI-SITE
Transforming Enterprise Security with TrustSEC’s FIDO2 Biometric Smartcards: A European Multi Site Case Study
In today’s digital-first business environment, enterprises face ever-increasing cybersecurity threats while striving to maintain seamless employee access to critical syst…
Read the case study →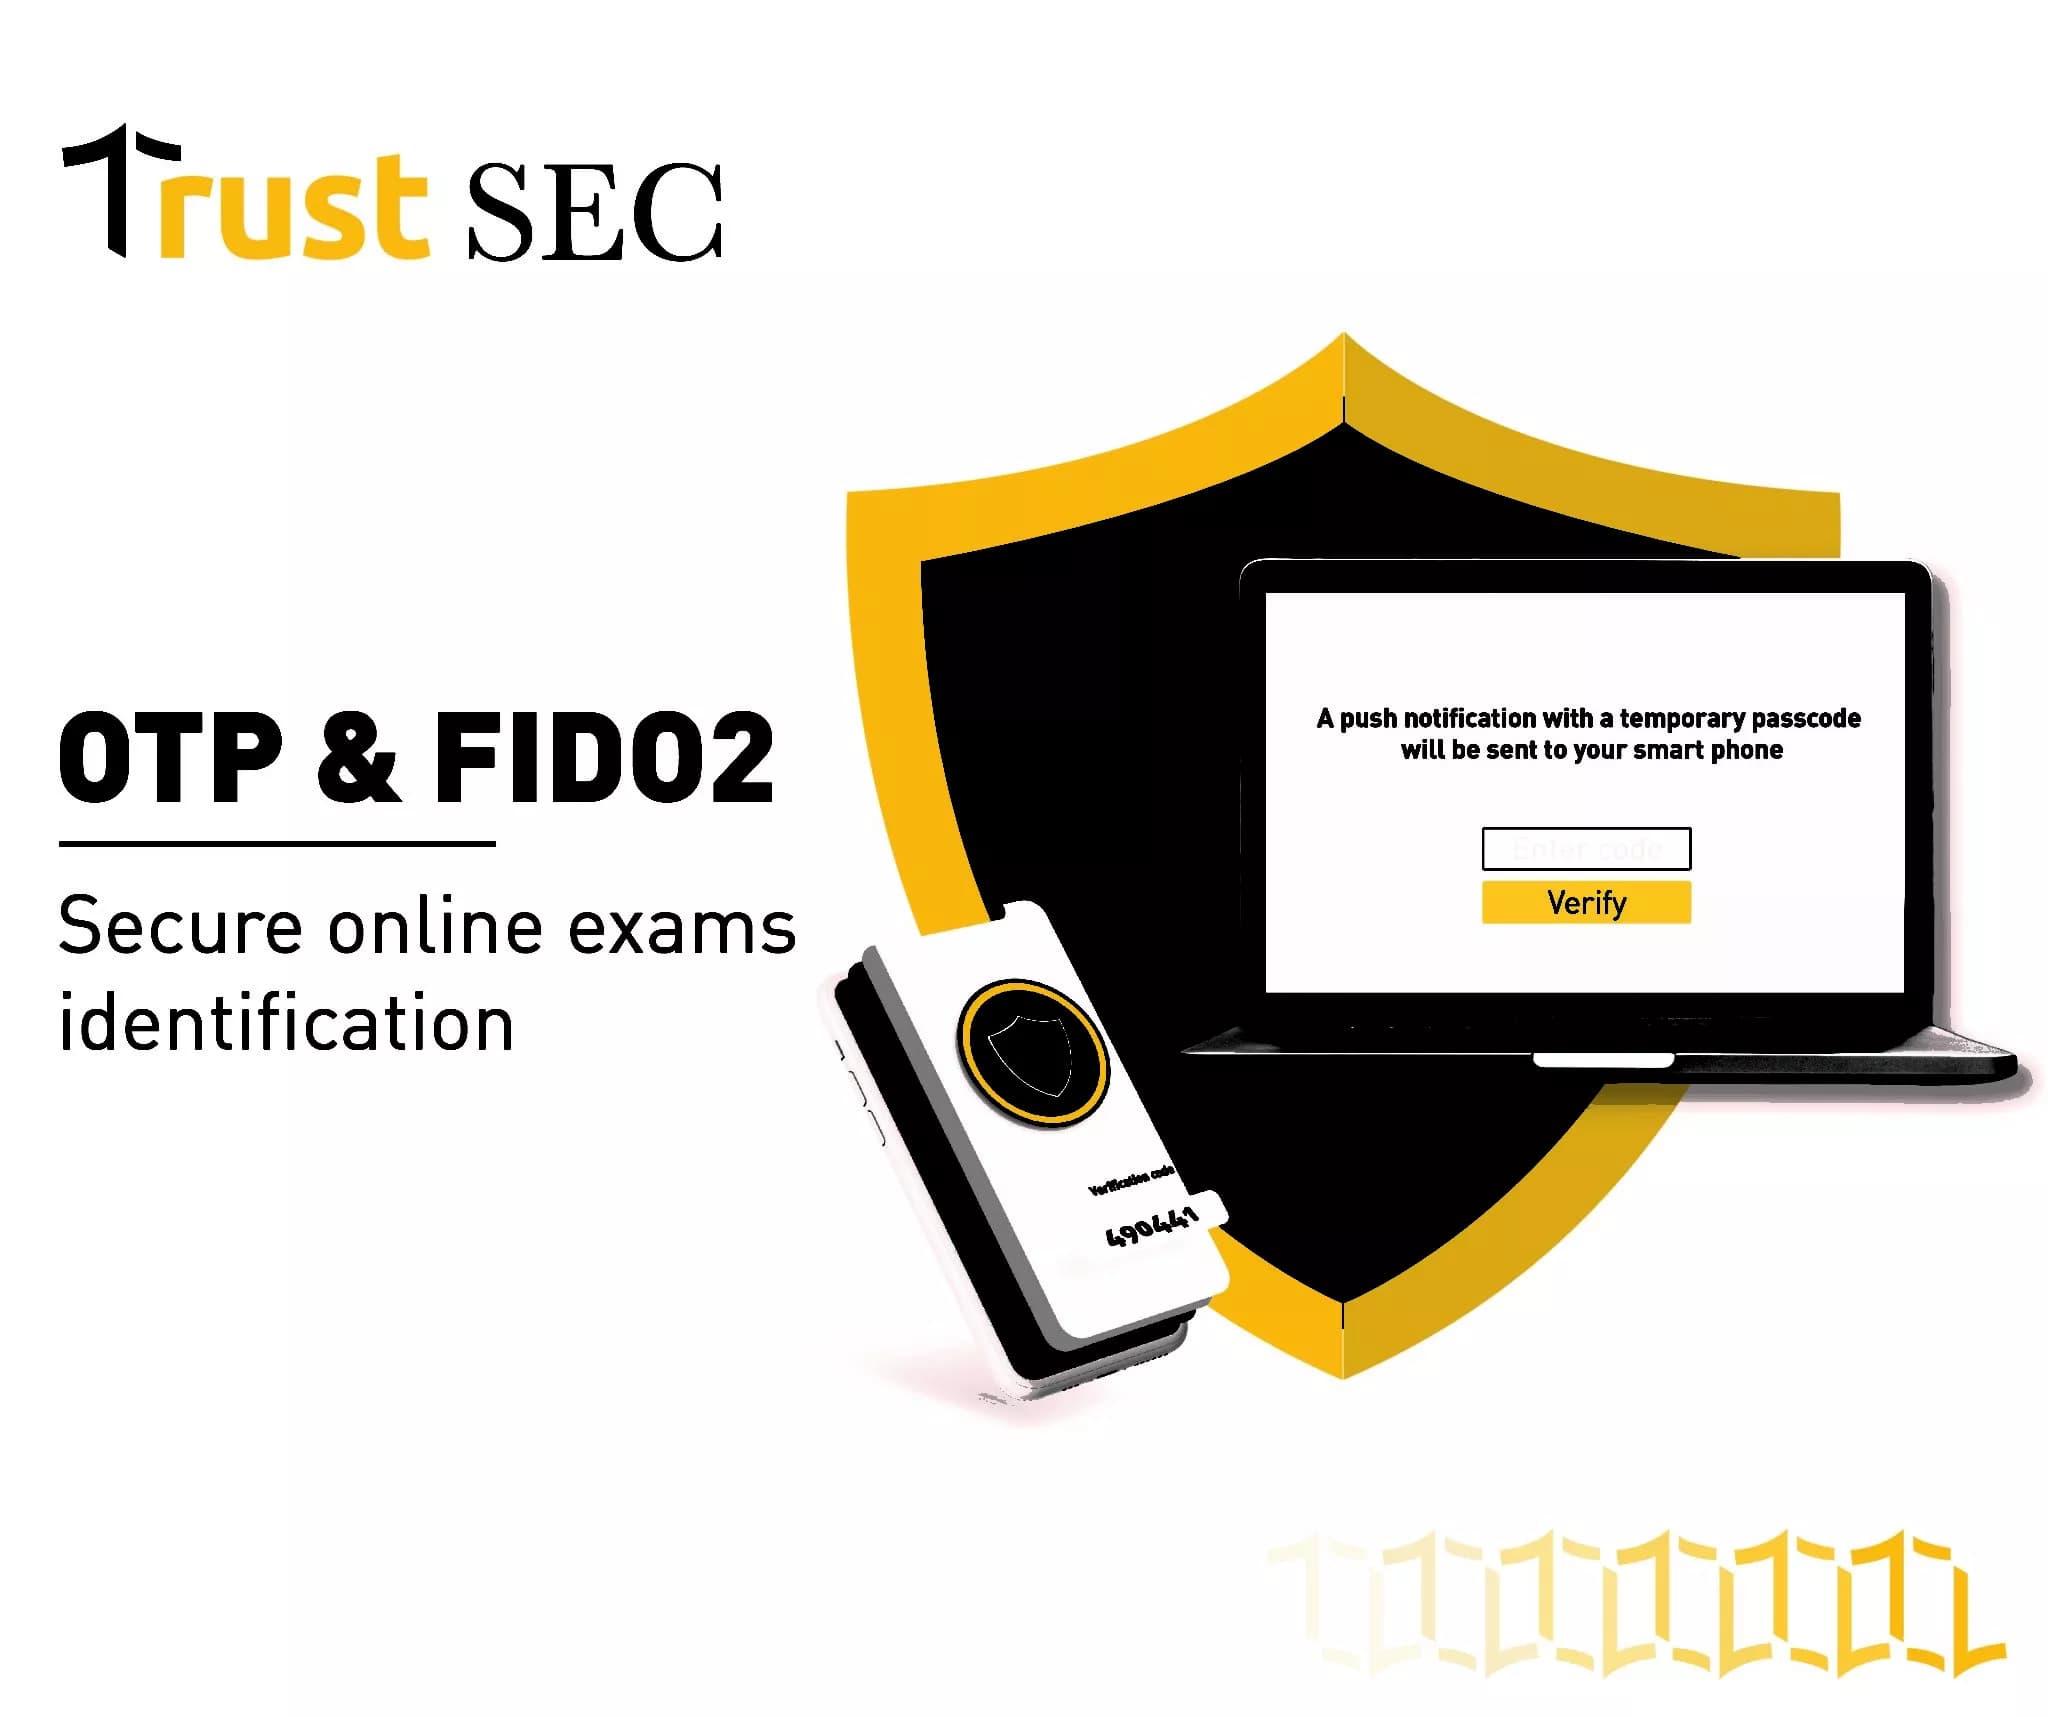 CASE STUDY · EDUCATION
COVID-19 and Secure online exams revolution!
The COVID-19 outbreak forced many countries to extend schools’ and universities’ closure to protect the safety and wellbeing of its employees, teachers, and students. The…
Read the case study →Our partners
Who we build and deliver with.
Technology partnerships with leaders in communication and information security, providing integrated, highly secure solutions.
Latest news
What we launched, and where to find us.
02 / THE COMMITMENT
Engineered, maintained and supported inside the Union.
All TrustSEC technologies are engineered, maintained and supported within the EU — ensuring full compliance with GDPR, eIDAS and local digital-sovereignty mandates.
From Szczecin to every member state: a team of cryptographers, engineers and an ICT lawyer who advised the European Union on eIDAS.